On June 1, 2026, the AICPA announced proposed 2027-2030 strategic plans for PEEC and the Peer Review Board. The consultation deadline was August 31, 2026.
PEEC promotes ethical behavior by AICPA members and others subject to the Code of Professional Conduct. The Peer Review Board oversees its practice monitoring program. Public-company audit committees should also assess the separate SEC and PCAOB requirements applicable to their auditor.
Both strategic plan proposals cite significant issues impacting accounting, including technology shifts such as the increased use of AI and automation, new business models and alternative practice structures, emerging areas of assurance such as sustainability and cybersecurity, the continued pace of mergers and acquisitions within the profession, and increasing business and regulatory complexity.
This article examines the strategic plan consultation and questions audit committees can use in oversight. The plan is separate from individual ethics interpretations and their adoption or effective dates.
The strategic plan consultation concerns PEEC's direction for 2027-2030. It does not itself amend the Code of Professional Conduct. Any specific future change requires its own standard-setting process and published terms.
What Is the AICPA PEEC and What Is It Proposing to Change?
The Professional Ethics Executive Committee serves as the AICPA's senior ethics committee and promotes ethical behavior for AICPA members through its Code of Professional Conduct. PEEC's strategic plan sets out the framework for how it will develop standards, support implementation, and engage with stakeholders over the four-year period beginning in 2027.
The PEEC's Code of Professional Conduct governs every CPA who is an AICPA member, whether they work at an audit firm, in a corporate accounting function, as a government accountant, or in another capacity. For public company auditing purposes, it governs the ethical and independence obligations of audit partners, senior managers, and other engagement team members at CPA firms.
The PEEC's proposed 2027-2030 strategy focuses on maintaining high-quality standards in the public interest, strengthening implementation support, enhancing stakeholder engagement, and modernizing operations. Key factors shaping the strategy include technological advancements such as AI, increasing regulatory complexity, evolving firm structures, expanding assurance needs including sustainability and cybersecurity, and the need for alignment across standards and oversight functions.
AICPA Vice President Carl Mayes described the current environment: "In today's practice environment, practitioners are navigating unprecedented levels of change. In the face of that complexity, these draft strategic plans for the AICPA's Peer Review Board and Professional Ethics Executive Committee provide CPAs with the clarity they need, outlining how we will continue to promote assurance quality and ethical conduct in the years ahead.
The strategic plan sets priorities. The consultation page identified August 31, 2026 as the feedback deadline. Monitor PEEC project activity for individual exposure drafts and final releases.
What Factors Shape the PEEC 2027-2030 Strategic Plan?
The consultation identifies technology, changing firm structures, expanding assurance needs, and regulatory complexity as factors shaping PEEC's strategy. Audit committees can use these factors to organize questions for their auditors.
The following questions are practical oversight considerations drawn from those factors. They should not be read as specific amendments announced by PEEC.
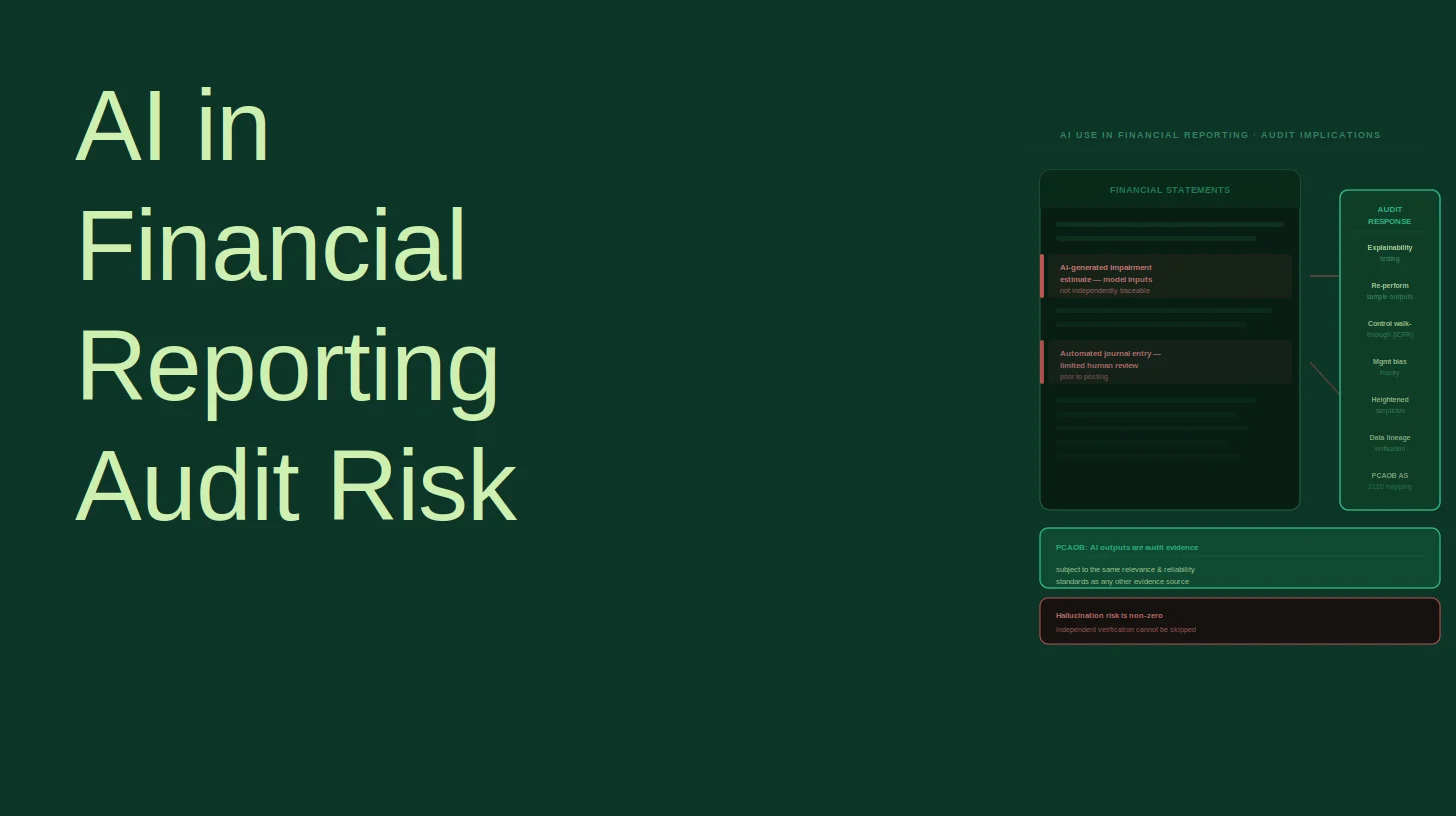
Technology and AI: which tools does the auditor use, who checks their output, and how are limitations and review procedures documented?
Alternative practice structures: how does the auditor assess independence across its ownership and affiliated entities? PEEC separately issued an alternative practice structures exposure draft, whose comment period closed April 30, 2026. Assess its project status and the applicable Code before treating proposed revisions as effective requirements.
Emerging assurance areas: what competence, independence, and confidentiality arrangements does the firm use for sustainability or cybersecurity assurance engagements?
M&A within the profession: the pace of accounting firm mergers, including both traditional firm combinations and PE-backed acquisitions, creates ethics and independence questions when merged firms have client relationships, former partners, or alumni relationships that affect independence under existing rules.
The AI Ethics Question: What Rules Apply When Your Auditor Uses AI in Your Engagement?
AI use raises practical questions about competence, review, confidentiality, and independence. Ask the engagement partner how the firm addresses those questions under its applicable professional requirements.
The specific ethics questions that AI raises for CPAs performing audit or attestation services:
Competence: who understands the tools used in the engagement, their limitations, and the judgments needed to review their output? Ask how the firm trains and supervises those staff.
Review: how are AI outputs checked against source evidence, how are errors handled, and who is accountable for the work included in the engagement file?
Objectivity and independence: ask how the firm assesses relationships between its tool vendors, affiliated entities, and the audit client, and how any identified threats are addressed.
Audit committees can ask which AI tools are used, how outputs are supervised and checked, and how the firm evaluates ethical and independence implications. Those questions are useful now; the strategic plan does not announce an AI-specific inspection checklist or a new obligation.
The PE-Backed Firm Independence Question: Which Requirements and Proposals Apply?
The AICPA's alternative practice structures exposure draft proposes changes to independence and related interpretations. Its comment period closed April 30, 2026. The PEEC project page identifies individual projects and releases; the strategic plan consultation should not be used as an effective-date source for a separate interpretation.
Ask the auditor which currently applicable requirements govern its ownership and affiliated entities, what threats and safeguards it has documented, and what proposed changes it is monitoring. The engagement partner should distinguish effective requirements from exposure-draft provisions when explaining the firm's compliance.
The Cybersecurity Ethics Question: What New Confidentiality Obligations Are Being Proposed?
Cybersecurity assurance is one of the fastest-growing practice areas for CPA firms. The SOC for Cybersecurity (System and Organisation Controls for Cybersecurity) framework developed by the AICPA allows CPA firms to provide attestation services on an entity's cybersecurity risk management programme. SOC 2 reports, which cover security, availability, processing integrity, confidentiality, and privacy, are increasingly required by customers, regulators, and investors.
The strategy identifies cybersecurity assurance as a factor affecting the profession. The following are practical questions for the committee to discuss with its auditor.
Confidentiality: how does the firm protect client security architecture, vulnerability, and control information accessed during cybersecurity assurance work? Ask about tool access, data handling, and vendor arrangements.
Independence: if the firm provides both cybersecurity consulting and assurance, ask how it assesses the relationships and work involved and documents its applicable independence analysis.
Competence: what experience and training support the personnel performing the cybersecurity assurance work, and how does the firm supervise their procedures?
For audit committees that rely on SOC 2 reports from service organisations, or that engage their own auditor for cybersecurity attestation services, the PEEC's cybersecurity ethics agenda is relevant to auditor oversight.
What Should Audit Committees of PE-Audited Companies Know About the Comment Period?
The consultation page set August 31, 2026 as the deadline and invited feedback from all stakeholders. That deadline has passed. Check later PEEC materials for the next opportunity to comment on a specific project.
Audit committees of companies whose auditors have PE ownership structures are specifically positioned to provide relevant input. The PEEC's standard-setting process benefits from input by those who observe the practical effects of ethics standards from the user side of the auditor relationship. An audit committee's perspective on how PE ownership affects auditor independence, communication, and quality provides information that PEEC staff may not obtain from firm-side or practitioner-side commenters.
The PEEC consultation paper page provides the proposal and submission information. Use the paper itself when evaluating its questions and priorities.
Audit committees do not need to be ethics experts to submit a comment. A one-page letter describing the audit committee's experience with PE-backed auditor independence, or its concerns about AI use in the engagement, or its questions about how cybersecurity attestation independence is governed, provides exactly the kind of stakeholder input the comment process is designed to elicit.
Should Your Company Submit a Comment Letter and What Would You Say?
Most companies do not submit comment letters on professional ethics standard-setting processes because they perceive those processes as being for accounting firms, not for corporate issuers. That perception is incorrect.
The AICPA Code of Professional Conduct governs the behaviour of the CPAs who audit your financial statements. The independence, objectivity, and competence requirements in the Code directly affect the quality of your audit. Audit committees have a direct and legitimate interest in how those requirements are set and enforced.
The three most relevant areas for an audit committee comment letter are:
PE-backed firm independence: document the audit committee's experience assessing ownership structures, auditor independence, and the information it receives from its auditor. Identify practical gaps that future guidance could address.
AI use in audit engagements: describe what the audit committee currently knows (or does not know) about AI tool use in its auditor's engagement. What information does the audit committee receive from the engagement partner about AI tool use, supervision, and output verification? What competence and due care disclosures would the audit committee find useful in assessing AI-assisted audit quality?
Cybersecurity ethics: if the company uses SOC 2 reports or engages its auditor for cybersecurity attestation, describe how the audit committee currently assesses independence in those engagements. What guidance from PEEC would make that independence assessment more straightforward?
For future consultations, verify the published submission instructions and deadline. A comment letter can explain practical oversight difficulties and the information that would help the audit committee assess its auditor.
What Is the Timeline From Comment Period to Final Ethics Code Changes?
A strategic plan does not provide a project-specific effective date. PEEC's standard-setting process includes public deliberation, exposure of proposed standards, and a formal vote. The published final release determines a particular change's effective date.
Track individual projects and their releases. The timing of each change depends on its standard-setting process and published effective date.
What Should Your Audit Committee Add to Its Next Meeting Agenda?
- Ask the engagement partner to explain applicable independence requirements and the firm's assessment of ownership and affiliate relationships.
- Discuss AI tool use, supervision, review, and confidentiality in the engagement.
- Assign an owner to monitor individual PEEC projects and bring proposed or final changes to the committee with their published status and dates.
Frequently Asked Questions
What is the AICPA PEEC comment deadline?
The strategic plan consultation set August 31, 2026 as the deadline. That consultation concerned the plan, and did not itself amend the Code.
What is the AICPA proposing to change about the ethics code for AI?
The strategic plan identifies AI and automation as factors affecting the profession. Specific Code amendments and effective dates should be established from individual project documents. The plan alone does not establish an AI rule change.
Does the PEEC proposal affect PE-backed audit firms?
Changing firm structures are relevant to PEEC's strategy. Audit committees should evaluate the auditor's applicable independence requirements and monitor the separate alternative practice structures project.
Should companies submit comment letters to the AICPA PEEC?
The consultation invited feedback from all stakeholders. Audit committees can provide practical input on auditor independence, AI use, and assurance work when a relevant consultation is open.
When will the new AICPA ethics code changes take effect?
Use each final release for its effective date. The strategic plan consultation does not establish when a specific new Code amendment will take effect.
Key Takeaways
- The consultation deadline was August 31, 2026. Monitor PEEC's individual projects for current status and further consultations.
- The strategic plan does not itself amend the ethics code or establish a project's effective date.
- Audit committees can ask practical questions about auditor ownership, independence, AI use, and cybersecurity assurance.
- Check the published status of the alternative practice structures project before treating its proposed provisions as effective requirements.